IRS Encourages Reporting of Tax Fraud, Scams, and Suspicious Activity
Employers should encourage employees to report suspicious requests involving payroll, tax documents, or employee information.
Fraudulent requests do not always look suspicious
HR and benefits departments routinely receive requests to update employee information, change payroll deductions, modify benefit elections, or share enrollment data with brokers and vendors. During busy periods, such as open enrollment and year-end processing, these requests can arrive in large volumes, making it easy to overlook warning signs.
Unfortunately, cybercriminals know that HR departments handle sensitive employee information and have access to systems that can affect benefits, payroll, and financial transactions. By impersonating employees, brokers, vendors, or company executives, attackers may attempt to convince HR personnel to disclose confidential information or make unauthorized changes.
The challenge is that fraudulent requests do not always look suspicious. They may appear to come from a familiar email address, reference an actual employee or vendor, or be part of an existing email conversation.
Cybercriminals use several techniques to make fraudulent requests appear legitimate. Some create email addresses that closely resemble those of employees or business partners. Others gain access to actual email accounts and send messages that appear to come directly from someone the recipient knows.
For example, an HR representative might receive an email that appears to be from:
Each request may sound reasonable, particularly when it references familiar business processes or creates a sense of urgency.
A common warning sign is pressure to act quickly, bypass normal procedures, or avoid contacting others before completing the request.
Many employees assume that an email is legitimate when it comes from a recognized sender. However, email accounts can be compromised, and attackers can manipulate sender information to make messages appear authentic.
Even an email that arrives within an existing conversation may be fraudulent if someone has gained unauthorized access to an account.
For this reason, HR personnel should not rely solely on the sender’s name, email address, or familiarity with the organization when evaluating requests involving sensitive information or financial changes.
The more sensitive the request, the more important independent verification becomes.
Employers should establish clear procedures for reviewing requests involving employee data, benefits administration, and financial transactions.
Verify unusual requests through a separate communication channel. If a request involves confidential information, payment instructions, or an unexpected account change, contact the individual or organization using a previously verified telephone number or established communication method. Do not rely on contact information provided in the suspicious message.
Follow established authorization procedures. Requests to modify employee records, change payroll deductions, or release sensitive information should follow the organization’s normal approval and verification requirements, even when the request appears to come from a manager or executive.
Limit the information shared. Before sending employee census files, enrollment records, or other sensitive information, confirm that the recipient is authorized to receive it and that the information is necessary for the stated purpose. Use approved secure methods for transmitting confidential data.
Be cautious about urgency and secrecy. Requests that demand immediate action, discourage verification, or ask employees to bypass established procedures should receive additional scrutiny.
Review unexpected changes carefully. Changes to payment instructions, bank accounts, vendor contact information, or administrative access should be independently verified before being processed.
Report suspicious requests promptly. Employees should notify their IT or security team when they encounter a potentially fraudulent message, even if they have not responded or disclosed information. If a request has already been acted upon, immediate reporting may help limit the consequences.
Security awareness is important, but employers should not depend entirely on individual employees recognizing suspicious messages.
Organizations can reduce risk by establishing documented procedures for sensitive requests, identifying who is authorized to approve changes, and requiring additional verification for higher-risk transactions.
HR departments should also review which employees and outside parties have access to benefits administration systems and ensure that access remains appropriate for their responsibilities.
During open enrollment, when employee information is frequently exchanged among HR teams, brokers, carriers, and administrators, these controls become especially important.
A fraudulent request does not always contain spelling mistakes, suspicious links, or other obvious warning signs. Sometimes it looks exactly like an ordinary business communication.
The safest approach is to verify before acting, particularly when a request involves confidential employee information, financial transactions, or changes to benefits records.
Taking a few additional moments to confirm a request through an established, independent channel can help prevent unauthorized disclosures, fraudulent transactions, and disruptions to benefits administration.
Benefit Allocation Systems (BAS) provides online solutions for: Employee Benefits Enrollment; COBRA; Flexible Spending Accounts (FSAs); Health Reimbursement Accounts (HRAs); Leave of Absence Premium Billing (LOA); Affordable Care Act Record Keeping, Compliance & IRS Reporting (ACA); Group Insurance Premium Billing; Property & Casualty Premium Billing; and Payroll Integration.
MyEnroll360 integrates with major insurance carriers for enrollment eligibility management (e.g., Blue Cross, Blue Shield, Aetna, United Health Care, Kaiser, CIGNA and others), and with leading payroll platforms for enrollment deduction management (e.g., Workday, ADP, Paylocity, PayCor, UKG, and others).
This article is for informational purposes only and is not intended as legal, tax, or benefits advice. Readers should not rely on this information for taking (or not taking) any action relating to employment, compliance, or benefits. Always consult with a qualified professional before making decisions based on this content.
Employers should encourage employees to report suspicious requests involving payroll, tax documents, or employee information.
October is Cybersecurity Awareness Month.
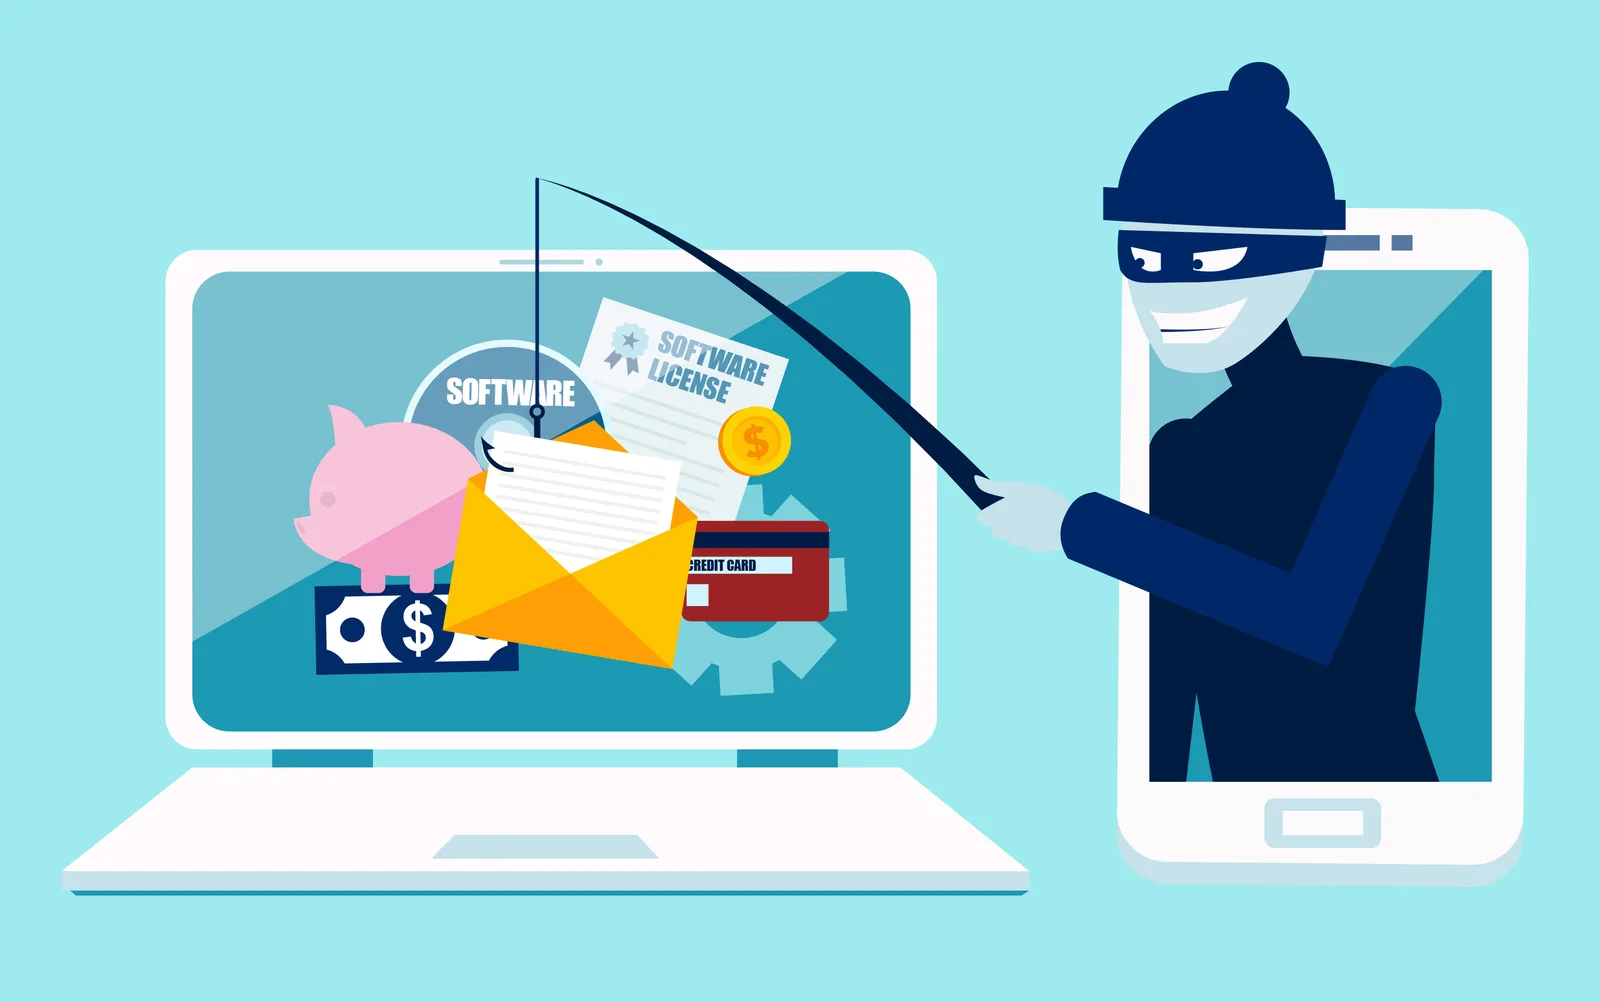
Open enrollment creates new opportunities for benefits-related phishing scams.